
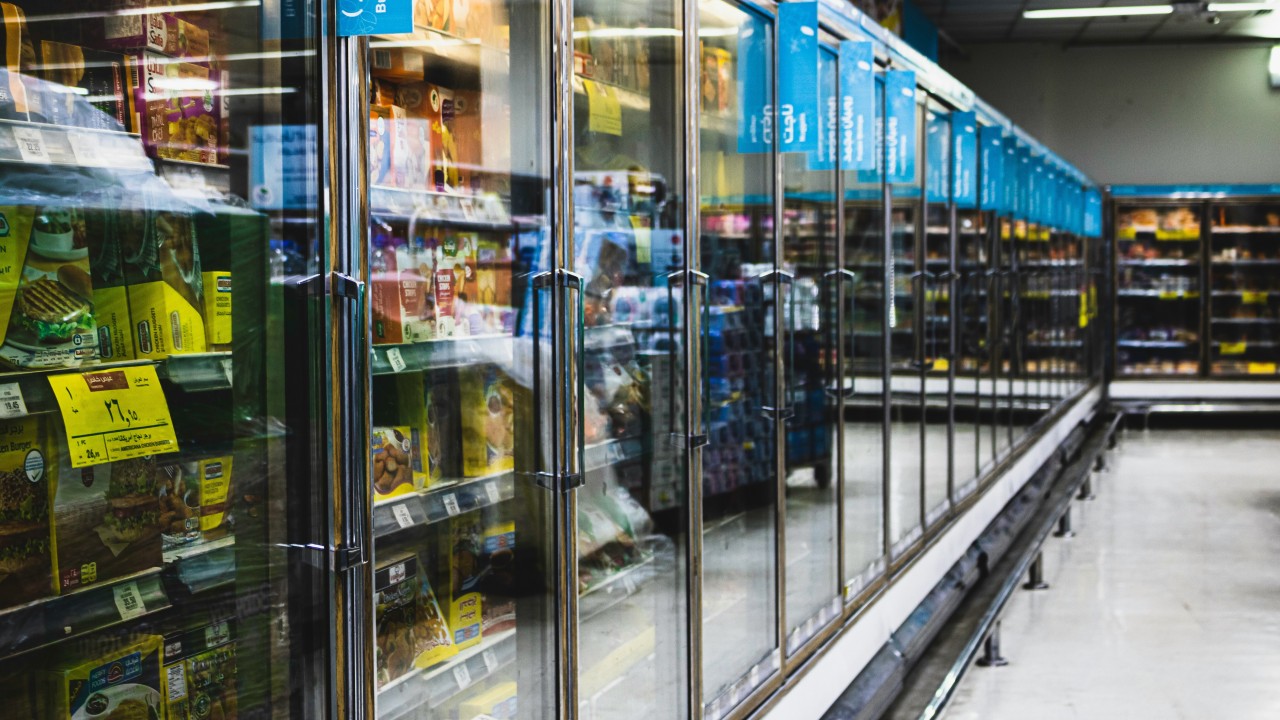
Overnight on October 11, attackers reached the refrigeration controls in hundreds of French supermarkets and pushed fully stocked cases into defrost. Intermarché, Coopérative U, Carrefour and several other chains reported spoiled stock, with some units reaching 50°C within six hours, according to CBS News. Reuters reports that France's national cybersecurity agency is investigating, and nobody has claimed responsibility.
Nothing reported so far suggests customer data was the goal. The losses showed up as product in dumpsters and empty freezer aisles, which is a very different crisis from the one most companies have prepared for.
For about fifteen years, cyber crisis plans have followed a well-worn sequence. You find the intrusion, work out whose personal information was exposed, notify regulators and individuals, and eventually, defend against the class action.
That work still has to happen, but the trouble is that it assumes the attacker wants your records, and a growing share of recent incidents have gone after the systems and assets a company needs to operate and earn revenue.
Beyond the customer database
Take-Two and Rockstar are dealing with a version of this right now. A leaker calling itself CyberLeek has been publishing footage from Grand Theft Auto VI for weeks and is threatening to release a full playable build before the November 19 launch unless the company ships physical discs and issues a formal apology, or the leaker's own crypto token reaches a $30 million market value. There is no public proof the full game is in anyone's hands, even though the leaked footage to date makes it seem highly likely that it is.
For Take-Two and Rockstar’s communications teams, that uncertainty doesn't make the job much easier. The leverage is the launch window itself, and the audiences that matter include investors, platform partners and a fan base already being warned about fake downloads that could compromise their devices.
Jaguar Land Rover shows what it costs when operations stop. After an intrusion in late August 2025, the company shut its systems down and halted UK production for about five weeks. It reported £196 million in direct costs for the quarter, and the Cyber Monitoring Centre estimated the wider hit to the UK economy at £1.9 billion across roughly 5,000 businesses. That same September, an attack on Collins Aerospace's check-in software led Brussels Airport to ask airlines to cancel about 140 flights in one day, even though the airport's own network was never breached.
Nova Scotia Power ended up handling both kinds of crisis at once. In early 2025 the utility notified about 280,000 customers that their personal data may have been stolen, then told its regulator that every customer might be affected. One of the harder problems turned out to be its smart meters, which kept recording usage but could no longer send it to billing. Customers were moved to estimated bills while contractors went door to door reading meters by hand, and complaints about inflated charges followed for months. A $133 million meter network approved partly on the promise of ending estimated bills spent most of a year producing them.
What communications leaders should do now
Each of these companies had a cyber response plan. It was probably pretty good, too.
Where they each struggled was in scenarios those plans never pictured, and its communications leaders themselves that are in a good position to close that gap before the next incident arrives.
Start with the scenario library
Most crisis manuals contain one cyber scenario, and it is a data breach. Add an outage that halts production or service, a compromised system that damages property or creates a safety risk, and a leak or theft of intellectual property, each with its own holding statement, approval path and spokesperson.
To build those scenarios properly, ask operations and IT for a plain-language list of the connected systems that would stop revenue if they failed. In a retailer that might be refrigeration and point of sale, and in a manufacturer the production line. Having that list in hand lets you brief leadership on business impact in the first hour of an incident.
Map your vendor dependencies with the same care
When the problem starts at a supplier, the media and customer questions still land on you.
In France, Danfoss acknowledged incidents affecting some of its refrigeration management systems, and every chain using that technology had to answer for it. Agree in advance with critical vendors on how quickly they will notify you and how public statements will be coordinated.
Decide ahead of time how leadership would handle demands that have nothing to do with ransom
CyberLeek is asking for a product decision and a public apology. A leadership team that has only rehearsed whether or not to pay a ransom will be debating corporate policy in real time, with the clock running.
Bring investor relations and finance into planning early.
An operational outage can become material long before anyone has counted affected records, and for public companies that can trigger timely disclosure obligations. JLR's quarterly results showed how quickly a factory shutdown becomes an earnings story, so investor language should be drafted alongside customer messaging.
Plan for an incident that lasts months….
Nova Scotia Power's problems ran well past a year. That isn’t an anomaly with cyber incidents. A first-week media plan will not carry you anywhere near that far, and long incidents need an update cadence, a record of every public commitment made and a bench of spokespeople who can share the load.
…. then rehearse with the people who run the business
A tabletop limited to IT, legal and communications tests the notification process. Adding store operations, plant managers and the CFO tests whether the company can keep functioning and explain itself while it does.
Customer notification and class action defence need to stay in every serious cyber plan
They were built for a time when the worst outcome of a breach was a list of exposed records, and they remain vital. But incidents are moving downstream and not reflecting that in the crisis plan can be a significant blind spot that results in a seven-figure bump to incident costs. The systems that keep food cold, cars moving down the line and meters talking to billing now sit on networks attackers already know how to reach, which means a single intrusion can hit revenue and market value long before anyone finishes counting records.
Communications leaders don't own those systems, but they will own the explanation when one of them fails. The best time to write that explanation, with operations, finance and key vendors at the table, is well before the morning the milk starts boiling in a balmy freezer aisle.
Recent Articles